SSL
HiTechCloud automatically generates and renews SSL certificates for all domains using Let's Encrypt.
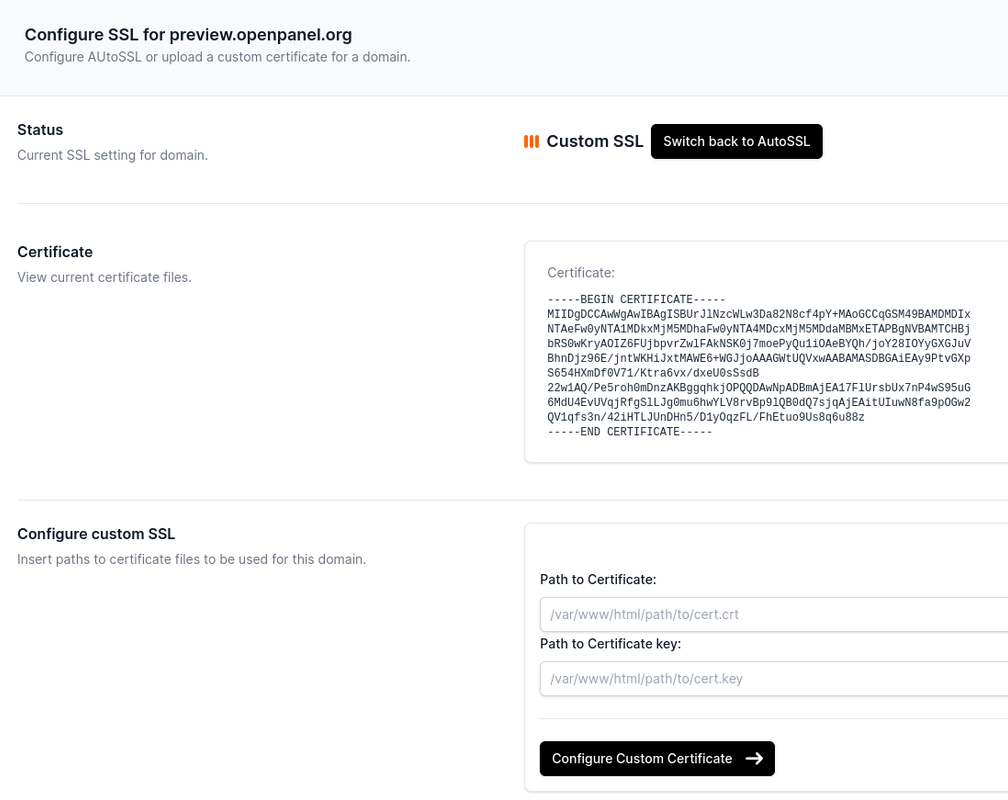
You can also configure a custom SSL certificate for any domain via HiTechCloud > Domains > SSL.
Custom SSL
To use your own SSL certificate:
- Go to HiTechCloud > Domains, then click SSL next to the domain.
- Under Configure custom SSL, paste the contents of your certificate and private key (PEM format, including the
-----BEGIN CERTIFICATE-----/-----BEGIN PRIVATE KEY-----lines) into the Certificate and Private Key fields. - Click Configure Custom Certificate.
Once configured, your custom certificate details will appear on the same page, and the SSL status will change to Custom SSL.
AutoSSL
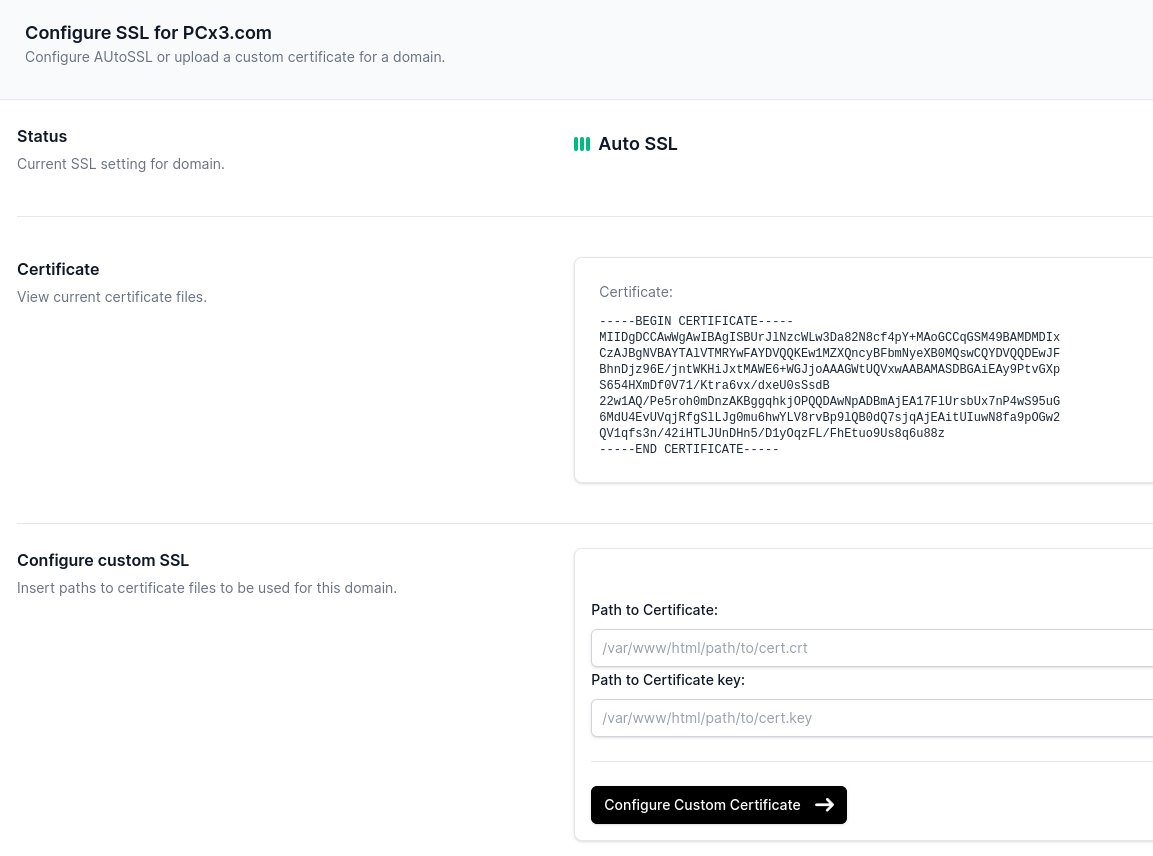
AutoSSL is the default option in HiTechCloud.
If you're adding a new domain, no action is required — a certificate is requested automatically the first time the domain is accessed over https://.
If the status shows Auto SSL but no certificate has been issued yet, click Generate now to reload the webserver and trigger issuance immediately.
To switch from a custom certificate back to AutoSSL:
- Navigate to HiTechCloud > Domains and click SSL for the domain.
- Click Switch to Let's Encrypt and generate.
This switches the domain back to AutoSSL and immediately attempts to generate the certificate. Once issued, it will be displayed on the same page.
Requirements
To ensure successful SSL generation:
- The A record for the domain must point to the server's IPv4 address.
- The DNS must be fully propagated. Use tools like whatsmydns.net to check.
- The domain must be accessed via
https://at least once to trigger certificate generation. Open the domain in a browser usinghttps.
If:
- The domain was just added,
- DNS is not yet pointed to the server, or
- The domain has not been accessed over
https://,
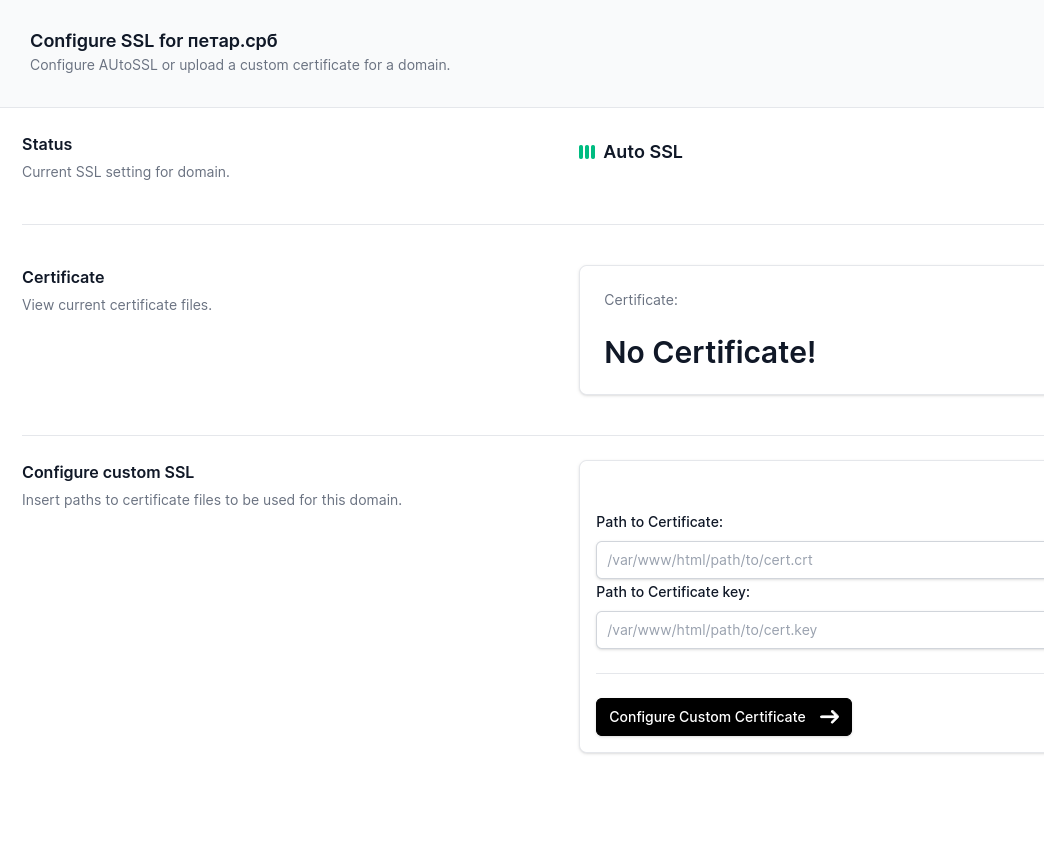
Then the SSL section will show “No Certificate!”
Wildcard certificates and DNS providers
A wildcard certificate (*.example.com) is proved with a DNS record. When this server hosts the domain's DNS, the panel answers that itself and there is nothing to set up.
When the domain's DNS is hosted somewhere else, open HiTechCloud > Domains > SSL for the domain and use the DNS provider section:
- Choose the company that hosts the DNS under Provider.
- The provider's credentials appear as one field each, named as the provider names them (for example
CF_TokenandCF_Account_ID). Fill in the ones your account with that provider uses; a provider that offers alternatives (an API token or a global key) only needs one set. - Click Save DNS provider, then Issue wildcard certificate.
Credentials are stored for the server's administrator account only, never in your own files, and are never shown again once saved: a field marked Set has a value on file.
To change a credential later, fill in only the field that changes. A field left blank keeps the value on file, so a token never has to be typed in again just because another one changed. To remove one stored value, tick Clear beside it. When nothing is stored yet, at least one field must be filled in.
Choosing a different provider starts afresh: the credentials stored for the previous provider are not kept, so fill in what the new one needs. Remove stored credentials deletes the provider and all its credentials.
On the command line, hitechcloudcli ssl dns-provider <domain> set <api> follows the same rules. Send the credentials as KEY=VALUE lines on stdin, so they stay out of the process list. Add --unset KEY to remove one stored key, or run hitechcloudcli ssl dns-provider <domain> unset KEY.